Tuesday, August 12, 2008

Passing The Dutchie @ Defcon 16

Like many things with this blog, I don't prioritize it above things like hanging out with my girlfriend, going to work, sleeping, breaking my iPhone, losing all my Defcon pictures, etc.

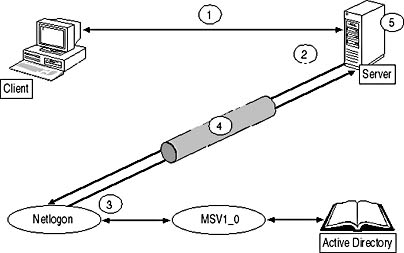
Last weekend was Defcon 16. I had a really great time speaking to a packed house on the death of NTLM. Slides, slide video and source code to Squirtle are now available for your pleasure. I'll be doing some more work and documentation on Squirtle shortly.

A few quick changes were made to the slide deck from what was presented (and the slides on the CD are waaaaaay something different :). Mostly added NTLM Signing as a mitigation and correctly stating that JoMoKun did the Samba Pass-The-Hash modifications. Sorry!

More updates coming.

Thursday, August 07, 2008

NTLM is Dead: Defcon 16


Friday, August 8th @ 2pm. Come learn how to own an enterprise with one XSS!

Slides and other material will be on-line after Defcon. Source code available here

Wednesday, July 30, 2008

Attacking NTLM

Defcon presentation times have been confirmed for a few weeks now and I've been slaving away at my slides and source code for a while now. I gave a pre-talk at work the other day and have decided to redo a lot of the slides. That's what you get when you ask for slides 38 days before the presentation. :)

Of course I'll have the full slides on-line after the conference but if you're coming to Defcon please come to my talk: Friday, August 8th at 2pm.

What exactly will I be talking about? Well, it's really difficult to describe succinctly but the best way I can say it is: An XSS inside your company == Total Domain Ownage.


Was that a scoff I just heard under your breath? Honestly, I'm not lying here. Because of the way NTLM and Windows Single Sign-On works your run-of-the-mill cross site scripting error on an internal resource can DEVASTATE your enterprise!

Stay tuned.

Friday, June 13, 2008

MS Cache and John the Ripper

Chalk this one up to knowledge remembered, forgotten, and then remembered again!

Lately I have been playing with using our MPI John the Ripper cluster to increase the crack rate of MS Cache passwords. With a very long list of passwords, some of which I knew would be easy to crack, I set out and started the process on 20 nodes. After a few days and ZERO cracks I started to wonder what the hell was going on.

The answer is one I knew many years ago when cachedump first came on the scene. The MS Cache encryption routine's salt includes the lower case username as part of the salt! Because some of the cachedump tools take the username out of the registry as-is and don't convert the case you'll run JTR for days with an invalid salt. No cracks for you!

So we can do a couple of things here:
  • Remember this next time and manually lowercase the usernames

  • Tell the authors to modify the tools we use to grab the cache hashes

  • Patch the tools ourselves (if we have the sources) and give them to the author

  • Modify the cracking program to always lowercase the usernames

John The Ripper's source code is really easy to fix and the quickest to do so a simple diff against mscash_fmt.c:

--- mscash_fmt.c 2008-06-13 15:56:07.000000000 -0700
+++ mscash_fmt-lower.c 2008-06-13 15:55:49.000000000 -0700
@@ -16,6 +16,7 @@
*/

#include
+#include

#include "arch.h"
#include "misc.h"
@@ -158,6 +159,9 @@

l = strlen(ciphertext);
strncpy(out, ciphertext + 2, l - PLAINTEXT_LENGTH + 1);
+ for(l=0; l < strlen(out); l++) {
+ out[l] = tolower(out[l]);
+ }
return out;
}


And now I don't have to remember this every time! JTR will remember for me and with a cluster of 20 nodes all running around 600,000 cracks a second maybe SOMETHING will crack. :)
Friday, June 06, 2008

NTLM, DefCon and Java!

John Heasman just posted a rocking method of obtaining NTLM hashes out of an enterprise by turning a Java applet into a web server! Check it out!

This year I'll be presenting at DefCon on the history of NTLM attacks, how they work and why we need to get rid of it. I'll release a tool that will combine as many hacks as I can get working to use captured users and their authentication tokens. There's been a lot of talk in the past few years about browser security and it's mostly hinged around using Javascript as a port scanner, sending attacks through the browser, attacking the platforms, etc. Few have been talking about an Enterprise-class risk and since that's what I get paid to think about I'm gonna blow it open. :) Come to DefCon and have a great time!

SyScan was great, a little small but helpful to bring the confidence up speaking to people who have no clue who I am! I learned quite a bit about my speaking style which helped firm up ideas about the DefCon presentation. I presented a combination of Web Security Mistakes including how to get a free MacWorld pass and spoke more about the future of PokeHashBall.

We stayed a few extra days to soak up the culture and soak the sweat into our clothes some more since this was our first trip to Hong Kong. The MongKok Computer Center was interesting but didn't seem to really have the deals I was expecting. I didn't get to any of the other computer centers however. Maybe next trip!

We went through Narita airport on the way back so I stopped at Duty Free and bought a bottle of Suntory Whiskey, the kind Bill Murray is hawking in the movie "Lost In Translation". For relaxing times, make it Santory time. . .


They have some of the greatest commercials.

Monday, May 26, 2008

Heading to SyScan Hong Kong


I've been given the opportunity to talk about Web Security at this year's SyScan conference in Hong Kong. This is my first trip to Asia so I'm really really excited about it! I haven't traveled much outside of North America -- the trip to Chaos Camp was my first oceanic flight. The Pacific Ocean is so huge that our flight from SFO will total 17 hours! It was only 9 hours to Dusseldorf!

This talk will expand on my OWASP talk on trusting the client and the MacWorld Pass hack. I'll also give a brief bit on NTLM Single Signon (NTLMSSP) attacks. Looking forward and will update at the con!

Friday, February 22, 2008

Your Client-Side Security Sucks

Last night I presented at the local OWASP chapter titled "Your Client-Side Security Sucks: STOP USING IT (as your only method of security)" and the turn-out was great. I met some really awesome people and the subject matter, while not cutting-edge research, appeared to hit home.

We, as Web Application people, are still making some simple mistakes. This presentation highlighted three REAL WORLD examples of client-side security done incorrectly.

The PDF slides are available here and soon I'll have a QuickTime video with a voiceover. I LOOOOOVE Keynote now! It has such useless transformations that you must pull back or else the content will be lost. How awesome is that? Plus exporting to a QuickTime so others can enjoy your ego-boosting flame build-in!

Rumor has it there will be an OWASP regional conference in the near future so hopefully I'll present this again with some improved slides and other real world examples. If you have any examples but don't want to "go public" yourself, let me know and I'll share them. This is one of the first things you're supposed to learn as a web developer so I have no problem exposing others. JavaScript, Java and Flash do not equate to protection! Shoot me an e-mail.

The second presenter, as luck would have it, is working on a tool exactly like I had done for NTLM relay attacks! We had a good chat about where we both saw our tools going in the future. It has renewed my energy in completing the PokeHashBall tools
at least. Thanks, eric!